Managed Zero Trust Service
Managed Zero Trust Service – the operating model for a Zero Trust security architecture
A Zero Trust model continuously validates every identity and every device before granting access to data or applications. With the Managed Zero Trust Service, Swisscom Broadcast offers a security solution that sets up, configures and monitors a Zero Trust architecture within organisations.
Using the Zero Trust operating model, Swisscom Broadcast verifies every access attempt based on the user, device and context. This blocks both vertical and lateral attack vectors in line with the principle ‘Never trust, always verify’. The solution enhances your security maturity and protects your digital infrastructures and AI applications from cyber-attacks, regardless of location, network, application or access profile. 360 degrees. Agnostic. Scalable.
AI-powered attacks breach traditional network boundaries in record time, rendering classic perimeter defence obsolete. This confirms the Zero Trust premise: no entity within the network deserves blanket trust. Fragmented security tools exist in isolation from one another, preventing centralised visibility. Without this visibility, no organisation can enforce consistent, context-based access decisions across its entire infrastructure.
Financial services providers
DORA has been mandatory since 2025, with supervision coming into effect in 2026. Yet, in the financial sector, it takes an average of 223 days to detect an attack – a timeframe that no perimeter can protect against.
Insurance providers
In interconnected partner ecosystems, every unverified login poses a risk to the brand and the customer base.
Healthcare and medtech
96 per cent of attacks steal data before it is encrypted. In hospitals, ransomware threatens not only records but also patient care – lateral movement becomes a matter of patient safety.
Energy and critical infrastructure
Since April 2025, the 24-hour reporting obligation has applied to critical infrastructure. But reporting is not a defence. Security of supply is achieved through segmentation before an attack spreads.
Industry/
Manufacturing
In global supply chains, unauthorised access is the largest unchecked vulnerability. New OT threat groups and ransomware are bringing production lines to a standstill. Where IT and OT converge, any unchecked access becomes a risk of downtime.
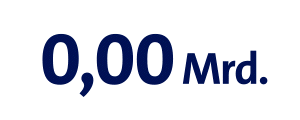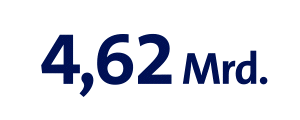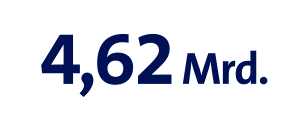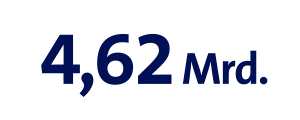
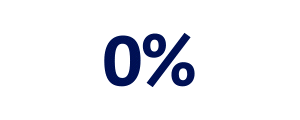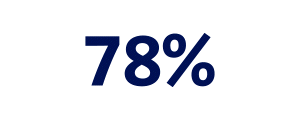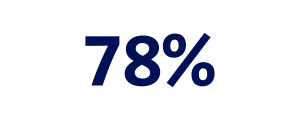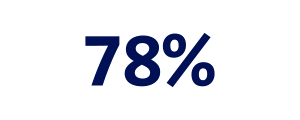
Cybersecurity in figures
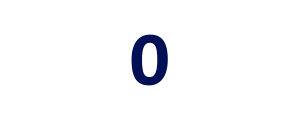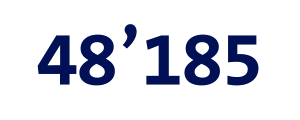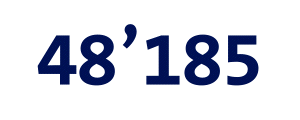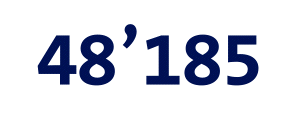
What zero-trust solutions does Swisscom Broadcast offer?
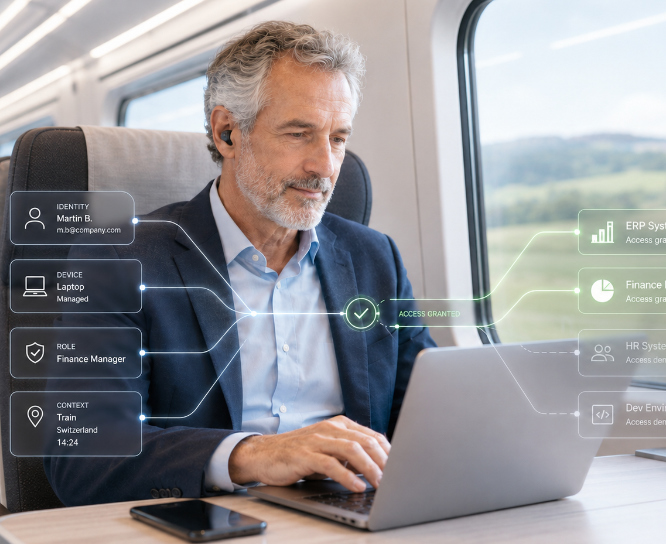
Identity-based
access (ZTNA)
Swisscom Broadcast guides you towards your bespoke solution to replace implicit network trust with identity-based access. This ensures that users and devices are granted only the rights required for a specific role in the relevant context.
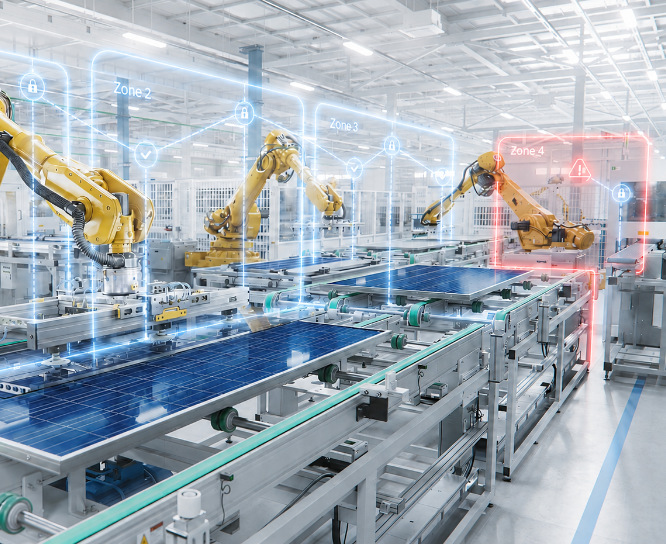
Microsegmentation
Swisscom Broadcast tailors microsegmentation solutions to your needs, ensuring that workloads and networks are segmented into isolated zones. This stops the lateral spread of a compromised endpoint before the damage can spread widely throughout the system.
Continuous Verification
Swisscom Broadcast’s agnostic solution portfolio offers solutions that re-verify identity, device status, location and context with every single request. As soon as the relevant signals change, access rights are revoked.
Policy Enforcement & Least Privilege
Based on the selected technologies, Swisscom Broadcast ensures the centralised implementation of least-privilege policies and makes access decisions consistent and traceable across identities, applications and AI interfaces.
How does Swisscom Broadcast plan, integrate and operate your zero-trust architecture?
Why choose Managed Zero Trust Services with Swisscom Broadcast?
Answers to frequently asked questions
What role does AI play in zero-trust architectures?
AI operates on both sides of a Zero Trust framework. On the attacker’s side, it accelerates reconnaissance, credential validation and exploitation. According to FortiGuard Labs, the time-to-exploit has currently fallen to an average of 24 to 48 hours. On the defender’s side, an AI-powered SOC automates threat detection, prioritises alerts in real time and reduces response times. Zero Trust utilises AI to derive dynamic, context-based access decisions from cross-system telemetry (identity, device status, location, context). Swisscom Broadcast integrates AI SOC solutions from leading providers such as Cloudflare and Akamai, thereby also protecting AI workloads and agent-based security scenarios. Crucially, AI does not replace the Zero Trust principle, but rather operationalises it. In doing so, it provides the signals that make continuous verification at machine speed possible in the first place.
What are the benefits of Swisscom Broadcast’s Managed Zero Trust Service?
Swisscom Broadcast builds, configures and operates your Zero Trust architecture as a managed service. This provides you with protection without tying up internal staff. The service is holistic: it combines identity-based access, microsegmentation and continuous verification into a 360-degree security net against vertical and lateral attacks. It is vendor-agnostic: Swisscom Broadcast integrates benchmarks such as Cloudflare, Akamai and Illumio, regardless of the manufacturer. And it is scalable: you can get started in small steps rather than as a major IT project. Swisscom Broadcast makes identity the control layer, limits the blast radius via least privilege, and makes risk reduction visible as a KPI. Operations and data storage take place in Switzerland, and compliance with requirements such as NIS2, DORA, FINMA and ISO 27001 is built into the service. The advantage is structural: Zero Trust becomes an operational model, not a one-off project.
Do I need to replace my existing security infrastructure, or can Zero Trust be integrated?
Zero Trust complements your landscape rather than replacing it. Swisscom Broadcast operates in a vendor-neutral manner and integrates existing identity providers, SIEM and endpoint systems into the Zero Trust architecture. The service consolidates fragmented security tools to provide centralised visibility. This is the prerequisite for consistent, context-based access decisions. Whereas traditional VPN grants implicit network trust, Swisscom Broadcast is gradually migrating to identity-based access (ZTNA). Existing investments remain usable and redundant tools can be consolidated over time, streamlining your vendor landscape. In the Zero Trust Readiness Assessment, Swisscom Broadcast determines which components are to be retained, integrated or replaced. This ensures a controlled transition rather than a ‘rip-and-replace’ approach.
Does the Managed Zero Trust Service also work for OT and legacy environments?
Yes. Zero Trust is particularly beneficial in OT and legacy environments, as the traditional air gap is increasingly disappearing and IT and OT are directly connected. Swisscom Broadcast segments production, OT and legacy zones using microsegmentation and stops the lateral spread of a compromised endpoint before it reaches critical control systems. For systems that do not themselves incorporate modern controls, Swisscom Broadcast shifts enforcement to the network and access levels: identity-based remote access for supplier maintenance replaces open remote maintenance channels. The approach follows recognised standards such as IEC 62443 and thus also addresses NIS2 as well as the Swiss reporting obligation for critical infrastructure. In this way, the service protects networked production without slowing down its operations.
How long does it take to implement a zero-trust solution that effectively defends against cyber-attacks?
Zero Trust is implemented step by step, not as a single, large-scale ‘big bang’. Swisscom Broadcast begins with a Zero Trust Readiness Assessment and prioritises, first and foremost, the measures offering the greatest risk reduction. These are typically identity-based access for critical applications and the segmentation of exposed zones. As a result, the first effective controls often take effect within weeks, not months. This approach has been deliberately chosen because rapid effectiveness is key. Swisscom Broadcast then gradually increases your security maturity through further building blocks such as continuous verification, microsegmentation and policy optimisation. The exact duration depends on the size, complexity and target architecture of your system and is set out in binding terms in the roadmap. Crucially, you gain protection incrementally and measurably from the very first building block.
How does Swisscom Broadcast measure effectiveness and risk reduction?
Swisscom Broadcast makes security visible as a KPI, meaning it is presented in a way that is suitable for the board rather than purely technical. The service measures the reduction in the attack surface, the limitation of lateral movement (blast radius) and defensive velocity: you gain transparency regarding the time taken for detection, containment and the revocation of compromised access credentials. It is precisely this speed that is regarded as the primary risk indicator in many surveys. Via a central control centre, Swisscom Broadcast provides live data and reporting that translates technical signals into business-relevant metrics for departments, management and the Board of Directors. Continuous verification and posture management provide ongoing evidence that the policies are effective. In this way, Zero Trust does not become a black box, but rather a verifiable risk reduction that you can demonstrate to regulators and governing bodies.